hAP · ax era
ax palette: a solid BLUE system LED dominates at power-on; during the hold the blue goes out and the small green flashes. The cue never moved — ignore the blue.
I bring a RouterOS device up from bare metal, lock it down, and keep a way back for when something breaks — and the fundamentals I run in production are the ones I have taught to a room of beginners.
Verified at the source — MikroTik’s own exam, the score confirmable on mikrotik.com.
The habits I drill into every student and set on every box before it carries a packet. The basics are boring on purpose — this is how they stay that way.
Lock the front door on day one
Before a box carries a single packet, its users, its services and its neighbour-discovery are pinned to the side of the network I manage it from — nothing answering the wide world that does not have to. The management plane is the first thing I close and the last thing I open: I would rather add an access rule back on purpose than find out months later what I left listening.
Know the way back first
I never touch a remote box without an exit already in place — a backup taken off the device, the reset-button windows in muscle memory, netinstall ready to go. Recovery is the first thing I set up, not the thing I improvise once the box is already dark and a plane ticket is the only other option.
Change under a net
Anything that could lock me out goes in under Safe Mode — provisional first, committed only once I have proven I did not just cut the line I am standing on. Drop the session and the box rolls the change back on its own. It is the difference between a mistake and an outage.
Backup is not export
A sealed, device-tied snapshot and a portable, readable script are two different tools for two different jobs: one restores this exact box, secrets and all; the other I can read, diff and re-run onto another. And the export default is version-dependent. RouterOS 6 wrote secrets into an export in clear text unless told otherwise, which is how the forums filled with rookies’ leaked credentials, pasted straight out of a config. RouterOS 7 flipped it to hide secrets by default, which broke migrations and long-trusted backup schedulers that had always captured them. Knowing which tool and which default the moment needs is half of config management.
The fundamentals fall into two shelves: the everyday muscle memory I use on every box, and the break-glass gear I reach for once a year and am grateful for every time. Both run at the depth I teach from.
The everyday muscle memory — how I get in, bring a box up, keep its config, and set the hygiene before it ships.
Into any box, several ways in.
WinBox, WebFig or key-based SSH for the day-to-day — and MAC-level access to the same device when its IP is gone, so a mislaid address is a nuisance, never a lockout.
Bare metal to online, in the right order.
WAN by DHCP, the LAN addressed, source-NAT masquerade last — the sequence that turns a factory-default board into a working router without the missing-masquerade dead end that strands most first configs.
The config in two forms, on purpose.
The tell that catches people is which artifact holds what: the certificate store rides only in the binary backup — a plain export drops it, and a reset wipes it — so an export-only disaster-recovery plan quietly loses your certs. The two forms are not interchangeable, and that is exactly where it bites.
A config import tested before it bites.
Since RouterOS 7.16 an import can be dry-run — verbose=yes dry-run walks the whole file and flags every syntax error without changing a single line (the verbose flag is mandatory alongside it). A big paste over the same link I manage the box through goes through the simulator first; only a clean pass gets committed for real.
A box that only answers to its keeper.
Logins, services and neighbour-discovery restricted to the management side by habit — the source-address locks and the discovery limits set once, on the way up, not after an incident. A caveat I teach: permissions apply at the next login, so a user demoted mid-session keeps the old rights on their open connection until it drops — revoking access is not instant.
The right box for the job, not the biggest.
Spec the device to the role, not to a spare-no-expense reflex: a flagship CCR gets bought where an RB5009 or an hEX carries the same traffic with headroom, because someone counted gigabytes of RAM instead of what the architecture and the cores actually do under load. The block diagram and the spec sheet decide it — mipsbe, mmips, arm, arm64 or tile, one fast core versus many, hardware offload or none — and reading them is the fundamental that separates a build that fits from money spent on cores that never move a packet.
The gear you reach for once in a year and are grateful for every time — bringing a dark or locked box back, usually from the far end of a VPN.
A bricked board, back from bare flash.
Netinstall talks to the boot loader over BOOTP on a direct link and re-lays a fresh RouterOS onto a device that will not boot — the recovery that turns a dead board into a delay instead of a replacement. When it stalls, the culprit is almost always the network, not the board: another DHCP server on the link — a second router, a VM’s virtual adapter, a laptop sharing its connection — answers the board before Netinstall’s own can, or an intermediary switch running DHCP snooping drops the offer. The fix is a direct link with nothing else handing out addresses, not swapping cables.
The reset button, read by feel and a count.
The hold time is the command — hold longer and it steps deeper: the RouterBOOT backup loader first, then a config-clear, then CAP mode, then the board handed to netinstall, no console, no menu to reach. And the LED is no clean per-stop code — steady at the backup loader, a flash only at the config-reset window, steady again at CAP, then dark — so a glance cannot tell you which side of that flash you are on. You count from power-on, not the glow.
A change that undoes itself.
People expect Safe Mode to be a staged candidate config they review and then commit. In fact the edits apply live the instant you make them, and it banks only a limited run of them before it forces a commit. It is a live safety net, so I pair it with the dry-run import for the changes it cannot cover.
Locked out at L3, back in at L2.
When the IP path is gone, MAC-Telnet and MAC-WinBox reach the device on the raw segment — a way in that does not depend on the thing that just broke. The caveat is MAC-Telnet’s alone: since the 6.45 overhaul its login is a zero-knowledge proof (the password never crosses the wire), but the session itself stays telnet-class with no cipher, so on a hostile segment what you type and see is exposed even though the password never was. MAC-WinBox does not share that gap — it is the WinBox protocol addressed by MAC instead of IP, so it keeps the same AES on the session either way.
The one thing recovery cannot buy back.
None of the three resets — software, hardware, or a full netinstall — recovers a forgotten admin password while keeping the configuration; netinstall makes the trade explicit, its "keep configuration" and password recovery mutually exclusive in one run. Lose the password and every way back costs you the config. I name the floor because knowing it is part of knowing the way back.
Sealed against hands you do not control.
For the high-stakes case — a device somewhere physical access cannot be trusted — Protected Routerboot seals the bootloader itself: the reset button, the pin-hole and the RouterBOOT menu all disabled, changeable only from inside RouterOS. It is the strongest lock I have, and I set it knowing the cost — forget the admin password behind it and there is no cheap way back, only a full NAND reformat and a netinstall. Anti-tamper you choose when physical protection outweighs the convenience of recovery.
The bring-up & recovery mechanisms, named
The primitives a bring-up or a rescue actually turns on — each one I run, not just know.
The rules I teach with a story attached, because I earned them the hard way — not from the manual, from the recovery afterwards.
Never flash a PoE chain in parallel.
I once kicked off a RouterOS upgrade across a set of PoE-chained RouterBOARDs at the same time — the smart move, or so it looked. The device powering the chain finished first and rebooted itself to apply the new version, and the instant it did it cut power to everything downstream of it, mid-write. The powered devices came back to half-flashed NAND: bricked, all of them, in one keystroke. Since then the rule is absolute, and I teach it the same way: stagger the upgrades, do the powered-downstream devices before the one that feeds them, and let each come fully back before you touch the next. On a chain you are never upgrading one box — you are upgrading its power supply too.
Safe Mode handed me a mistake back — from another continent.
I was on a wireless-ISP customer’s network over a VPN, a continent away, rotating the encryption key on a point-to-multipoint nv2 link — a long-range 5 GHz radio out on a remote tropical island. Get a key rotation wrong on the far side of a wireless link and you drop it, and there is no second way in: the fix would have been a boat or a helicopter and a pair of remote hands that do not exist out there. But the change was in under Safe Mode, so when the link fell and my session with it, the radio quietly rolled the change back and came up on the old key. I reconnected as if nothing had happened. RouterOS 7.18 later made Safe Mode scriptable — an auto-revert you can build straight into a script — which turns it into a deterministic fail-safe for automated and AI-driven changes, exactly the kind of guardrail an unattended change most needs.
My open RouterOS safe-mode reference on GitHub (tarikin)A MikroTik reset button has no menu — the hold is the command and the LED is the cue. Pick what you need; the board below counts with you, the way I walk remote hands through it.
field note On ax boards a solid BLUE lights first — ignore it. The cue is the small green.
hAP ax² · hAP ax³ · hAP ax lite (2022+) · Small recessed reset button — a pin, gently. Not the mode/WPS button beside it.
The trap shelf — field-earned, sourced:
hAP · ax era
ax palette: a solid BLUE system LED dominates at power-on; during the hold the blue goes out and the small green flashes. The cue never moved — ignore the blue.
hAP · ac era
ac palette: two green LEDs (pwr + usr), no blue anywhere (field). The original hAP ac (RB962) still carries a boot beeper; the ac²/ax refreshes are silent.
hAP
Dark mode looks like death
A runtime press of mode/WPS blacks out every LED by default — the board is fine.
hAP
CAP-overshoot recovery
Not another reset: connect WinBox by MAC, then QuickSet → Home AP (field).
hAP
The ax flash is late
On ARM64 boards the first green flash can arrive ~10 s after power (field).
hAP
Hidden rungs still fire
Two-rung ax manuals climb the whole ladder — the solid-LED CAP rung is real.
fleet
The LED is the command
Official pages disagree on every second-count — MikroTik’s own live manual now teaches the LED sequence. Release on the transition.
fleet
Manuals under-print the ladder
The rung count is a doc-template artifact — the field reliably reaches rungs the manual omits.
fleet
Four identities, one button
Before boot it is the ladder; on a running board it is WPS, a script hook, or a confirm-press — never a reset. 30-30-30 folklore does not apply.
fleet
The reformat hold nukes NAND
Hold ≈20 s into the reformat window and everything is irreversibly erased, RouterBOOT settings included — Netinstall becomes mandatory.
fleet
v7.17: the button says “yes”
device-mode wants a physical press to CONFIRM — a soft reboot never counts. That press is a signature, not a reset.
fleet
Two depths before power
Release at ≈3 s = boot the frozen backup loader; keep holding to LED-off = Netinstall via that loader. Two rescues, one gesture.
fleet
Netinstall’s port precondition
ether1 · ETH12 · MGMT/BOOT — by model. A server on the wrong port is the signature dead-end.
fleet
Trust the Product code
“hEX S” is two different boards; CSS326 is not CRS326. The spec-table Product code row is the resolver.
fleet
Dead buttons are usually policy
enable-jumper-reset=no kills half the button; protected-routerboot kills all of it. Check both before an RMA.
hAP ac³ numbered ladder + the generic Reset Button doc; the ax palette is field-convergent across ≥4 independent threads. Seconds are approximate and official pages disagree — the LED transition is the command. Built on a per-model table drawn from MikroTik’s manuals; check your exact SKU’s page (by Product code) before a production board.
Pick your board — or just press its button and feel the ladder.
Before you hold a real button, run the ladder on my reset-button simulator — six RouterBOARD archetypes, released on the LED transition. Open the standalone simulator →
The fundamentals stopped being basic for me the summer I had to teach them. You cannot teach what you only half-know — a room of beginners finds every gap in an afternoon.
A month building an MTCNA course by hand, for a cohort in Vietnam.
I founded the first authorized MikroTik training center in Vietnam, and to run it I spent more than a month hand-building the MTCNA material — every bring-up, every recovery, every quirk, written out so a beginner could follow it. A room of Vietnamese beginners taught me something no manual would — stay in ASCII at the console; diacritics and other non-Latin input can misbehave the moment you are inside the CLI, and a class learns that the hard way in an afternoon. That is where the fundamentals became reflex.
Teaching showed me the basics I take for granted are earned fluency — and one talk showed me how fast a small one, gotten wrong, costs you.
The tricks had become muscle memory — mac-telnet in when the IP is gone, RoMON to a box with no address, the reset-hold windows read by feel — things I had stopped noticing I knew, until a beginner’s “obvious” question showed me the obvious answer was fluency I had paid for without noticing. Moscow, 2017, barely a year in, taught me the flip side. I rebuilt a wireless-audit case in WinBox screenshots for a talk and missed one fundamental: I had captured them under a full-permission user, so fields a read-only account would have greyed out were editable. The senior engineers spotted it in seconds, and the whole story lost its weight — one basic, wrong, and the people who know the platform stop believing you. That is why I treat the fundamentals as sacred: they are the fluency I trust most, and the first thing an expert checks.
A photo from the MikroTik training room in Vietnam — coming soon
The fundamentals are the part nobody notices until they break. I keep them boring on purpose — every box reachable, recoverable, and the same one I would hand a student.
The fundamentals are the ground everything else is built on. The domains that stand on them, and the exam that verifies the depth.
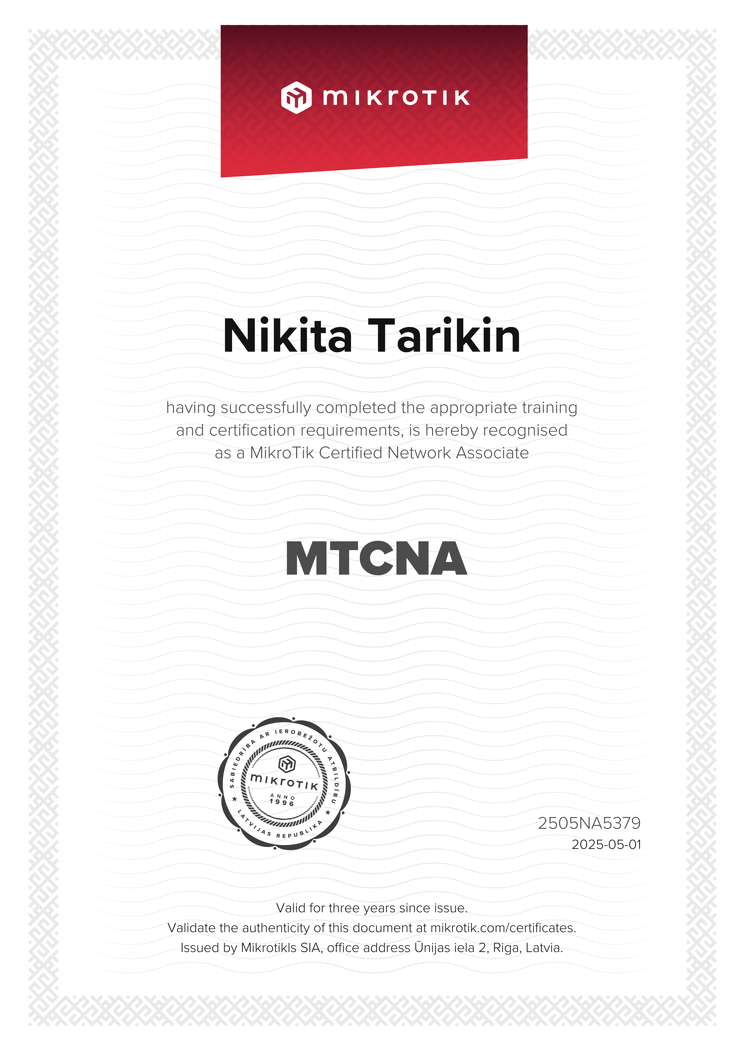
This is the issued MTCNA certificate — the network-associate foundation behind everything on this page, shown whole.
Certificate ID 2505NA5379 — cross-checkable on mikrotik.com.
Bring the box — a fresh deployment, a fleet upgrade you want done without bricking it, or a device that will not come back. I will scope it.
Scope a bring-up or recovery