MTCSE98%Active
MikroTik Certified Security Engineer
Valid May 2025 – May 2028 · Verify on mikrotik.com
I architect, harden, and audit network security posture across firewall, VPN, and access control.
What this certification validates
98% security score. Firewall architecture, IPsec VPN, certificate management, attack mitigation — each layer tested under exam conditions.
- ·Firewall filter chains (input/forward/output)
- ·NAT (srcnat/dstnat) advanced
- ·Mangle & connection tracking
- ·IPsec IKEv1 & IKEv2
- ·Certificate management (SCEP, CRL)
- ·RADIUS & EAP authentication
- ·Bridge firewall
- ·Attack detection & mitigation
- ·Cryptographic protocol selection
- ·Security audit methodology
MTCSE vs Cisco CCNA Security / CompTIA Security+
| Dimension | MTCSE | Cisco CCNA Security / CompTIA Security+ |
|---|---|---|
| Scope | RouterOS firewall, VPN, crypto — implementation | Broad security theory + vendor config |
| Vendor lock | MikroTik only | Multi-vendor / vendor-neutral |
| Hands-on depth | Full firewall rule building on real RouterOS | Mostly theoretical with some lab |
| Renewal cycle | 3 years, re-exam | 3 years, CE credits |
| Focus | Implementation-first (build the firewall) | Theory-first (understand the concepts) |
Certification combinations
MTCSE combines with these certifications.
Case studies
Anonymized engagements demonstrating this expertise.
Case #1
- Situation
- Multi-office enterprise needed IPsec mesh VPN across 12 sites with certificate-based authentication and automatic failover.
- Challenge
- Mixed IPv4/IPv6 networks with NAT traversal requirements. Previous flat IPsec config had single points of failure.
- Methodology
- IKEv2 with MOBIKE for mobile worker roaming, per-tunnel routing marks for traffic isolation, redundant peers with DPD-based failover, SCEP certificate enrollment.
- Result
- 99.97% VPN uptime over 18 months. I automated certificate rotation; site failovers required zero manual intervention.
Case #2
- Situation
- Client suspected ongoing network intrusion after their monitoring flagged unusual traffic patterns.
- Challenge
- No logging configured. Firewall rules were permissive defaults from initial setup years ago.
- Methodology
- Full firewall audit: rebuilt filter chains with explicit allow/deny, enabled connection tracking, added rate limiting for SSH brute-force and ICMP flood, configured syslog forwarding.
- Result
- Blocked brute-force SSH attempts from 3 identified IP ranges. Replaced permissive defaults with explicit allow/deny firewall policy. Configured syslog forwarding to a central collector.
Exam details
Exam format and certification details
- Format
- 25 multiple-choice questions, open-book
- Pass score
- 60%
- Duration
- 60 minutes
- Prerequisite
- MTCNA (can be expired for recertification)
- Training
- 2 days
- Validity
- 3 years
- Global rarity
- ~500–1,000 active holders
- RouterOS ver.
- RouterOS v7
Score history
Score progression across certification cycles
2019Kuala Lumpur
2022Bangkok
2025Bangkok
Training providers: Citraweb (ID), MikroTik SEA
Certificate
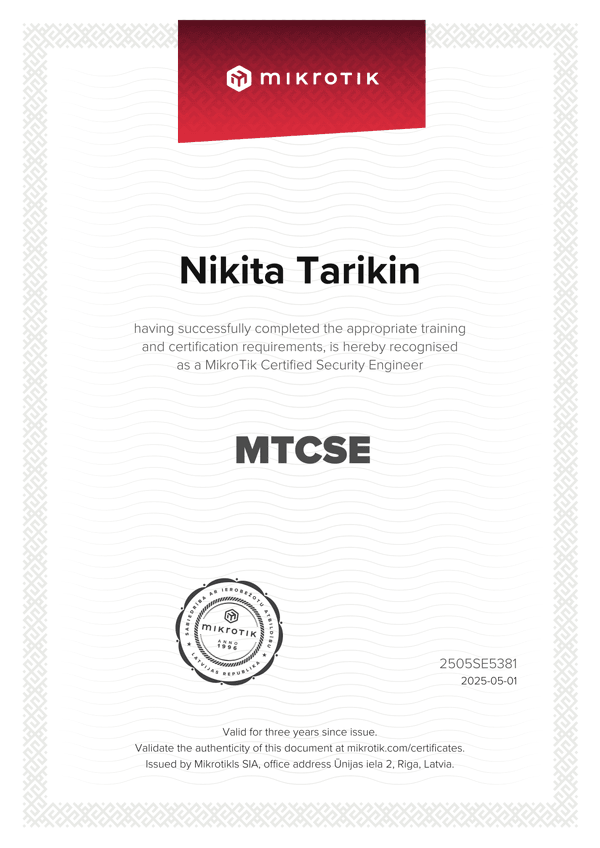
Click to enlarge
FAQ
What does MTCSE certification cover?
MTCSE validates advanced RouterOS security: firewall filter/NAT/mangle chain architecture, IPsec VPN (IKEv1/IKEv2), certificate management (SCEP/CRL), RADIUS/EAP authentication, bridge firewall, attack detection, and cryptographic protocol selection.
How is MTCSE different from CompTIA Security+?
MTCSE is implementation-focused — you build firewall rules and VPN tunnels on RouterOS hardware. Security+ covers broader theoretical security concepts across vendors. MTCSE goes deep on network device hardening.
What projects require MTCSE-level expertise?
I work on firewall audits, IPsec VPN deployments (site-to-site and roadwarrior), certificate-based authentication, intrusion detection, and compliance-driven security reviews.
How do I verify a consultant's MTCSE certification?
Verify on mikrotik.com/certificates using the certificate ID. MTCSE requires MTCNA as prerequisite.
Is MTCSE certification still relevant in 2025?
Yes. WireGuard integration in RouterOS v7 and IKEv2 improvements expanded the attack surface MTCSE covers — the scope grew, not shrank.
See how this expertise applies → Contact
Need MTCSE expertise?
Let's talk →